
 10 mins
Aug 28, 2025

DevSecOps brings security practices into the development and delivery lifecycle through automated testing, security controls, policy enforcement, monitoring, and continuous feedback.
For FinTech teams, this approach can help integrate security into CI/CD while creating repeatable controls and evidence across the software lifecycle.
NIST’s 2026 DevSecOps guidance similarly frames DevSecOps around implementing secure software development practices through modern development and delivery pipelines.
This guide explains how to use DevSecOps for FinTech to strengthen application security, support compliance requirements, secure software supply chains, and build a more controlled CI/CD environment.
FinTech teams ship software across payment systems, banking APIs, mobile applications, cloud infrastructure, and third-party services – all while handling sensitive financial and customer data.
That creates four core pressures:
1. Security: Vulnerabilities across code, dependencies, APIs, containers, and infrastructure need early detection.
2. Compliance: Requirements such as PCI DSS 4.0.1 and DORA increasingly intersect with software development, access controls, change management, and security testing.
3. Software Supply Chain: Open-source dependencies and third-party components require greater visibility and continuous monitoring.
4. Release Velocity: Security checks need to keep pace with frequent deployments without creating manual bottlenecks.
DevSecOps brings these concerns into the software delivery lifecycle.
By integrating automated security testing, policy controls, vulnerability management, and audit evidence into CI/CD, FinTech teams can build security into the delivery process rather than treating it as a separate release-stage activity.
DevSecOps can strengthen FinTech security across several layers of the software lifecycle.
| Application code | SAST, code review, security testing |
| Dependencies | SCA and vulnerability scanning |
| Secrets | Secret detection and centralized secret management |
| Infrastructure | Infrastructure-as-Code security scanning |
| Containers | Image scanning and artifact verification |
| Software supply chain | SBOM, provenance and dependency controls |
| CI/CD | Pipeline security gates and access controls |
| Cloud | Configuration and policy checks |
| APIs | Authentication, authorization and security testing |
| Production | Monitoring, vulnerability management and incident response |
| Compliance | Automated controls and audit evidence |
Compliance requirements increasingly intersect with software development, infrastructure, access management, vulnerability management, change management, and operational resilience.
DevSecOps gives FinTech organizations a mechanism for implementing many of these controls directly within engineering workflows.
For organizations handling payment card data, PCI DSS remains a critical security framework.
DevSecOps in FinTech can support relevant PCI DSS activities through:
→ Secure software development practices
→ Application vulnerability testing
→ Code review
→ Dependency management
→ Web application security testing
→ Access control
→ Logging and monitoring
→ Change tracking
→ Vulnerability remediation
→ Security testing within CI/CD
The important distinction is that DevSecOps supports implementation and evidence collection; it does not automatically make an organization PCI DSS compliant.
For financial entities operating in the European Union, the Digital Operational Resilience Act (DORA) introduces requirements around ICT risk management and digital operational resilience.
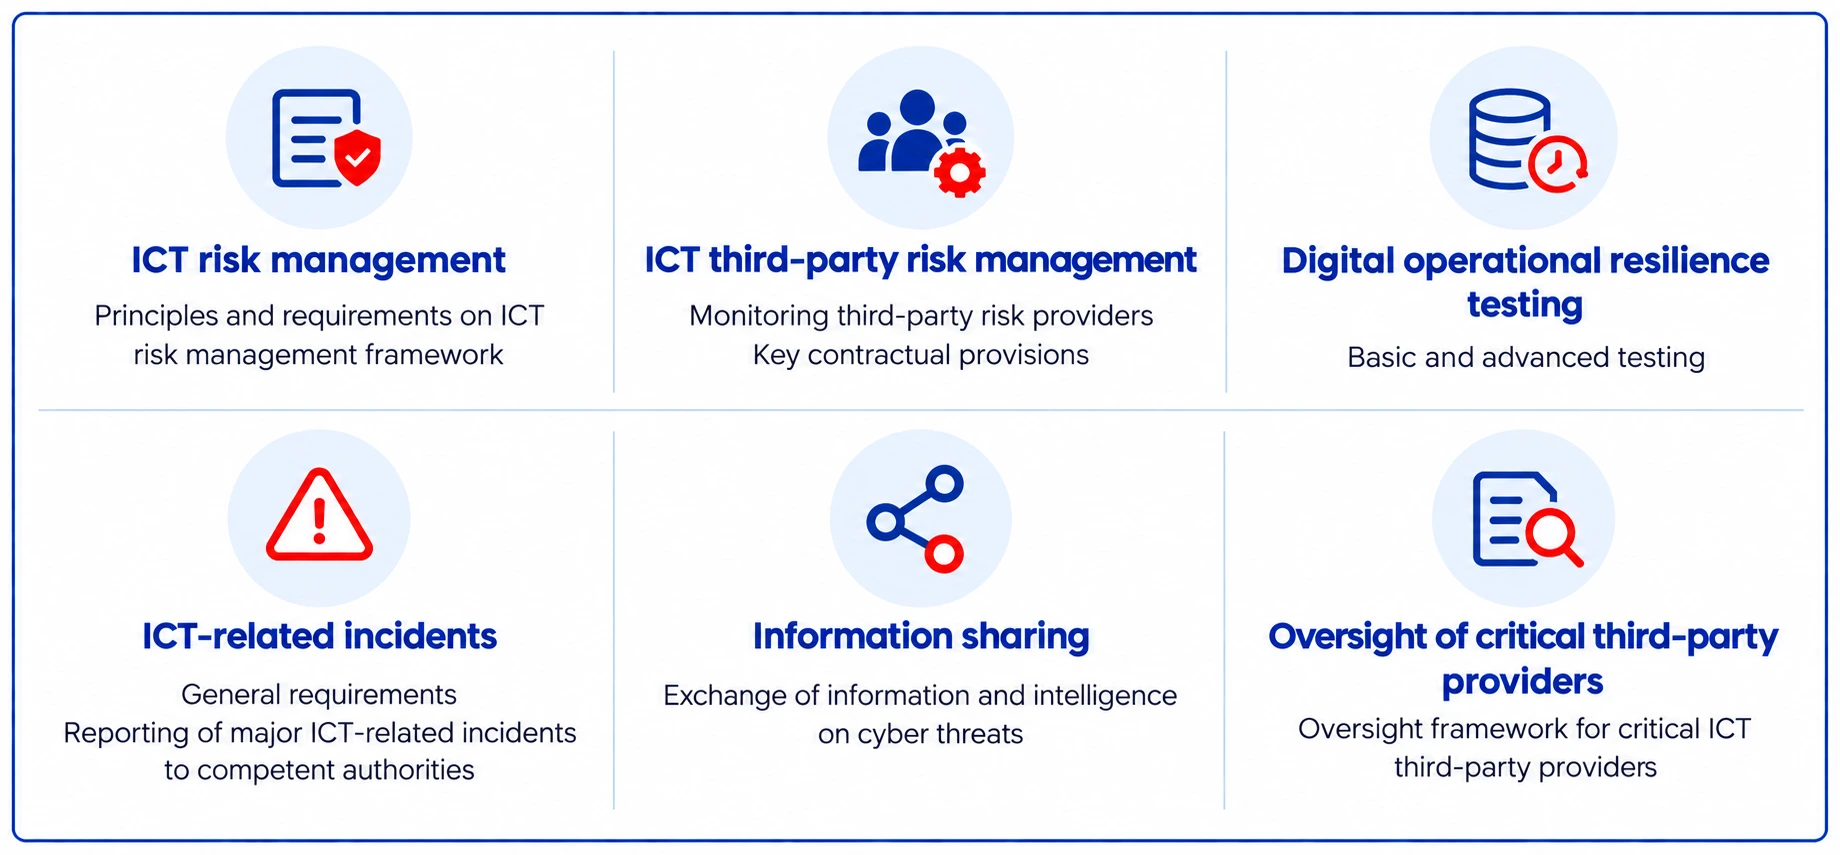
The European Banking Authority notes that harmonized DORA requirements apply across sectors including banking, securities and markets, insurance, and pensions.
DevSecOps for FinTech can support DORA-related operational practices through:
→ Controlled software releases
→ Vulnerability management
→ Infrastructure security
→ Access controls
→ Continuous monitoring
→ Incident response workflows
→ Change tracking
→ Security testing
→ Automated evidence collection
For organizations subject to DORA, these capabilities can become part of a broader ICT risk management and operational resilience program.
FinTech companies may also operate against frameworks such as SOC 2 and ISO/IEC 27001 depending on their customers, geography, business model, and contractual requirements.
DevSecOps in FinTech can help operationalize controls around:
→ Access management
→ Change management
→ Security monitoring
→ Vulnerability management
→ Secure development
→ Configuration management
→ Audit trails
→ Incident response
IBM’s financial-services DevSecOps architecture demonstrates this model by using CI, continuous deployment, and continuous compliance pipelines, with evidence collected across pipeline activities to support audit requirements.
A FinTech DevSecOps pipeline can integrate security checks from source code through production.
Plan → Code → Build → Test → Verify → Deploy → Monitor → Respond
A simplified implementation looks like this:
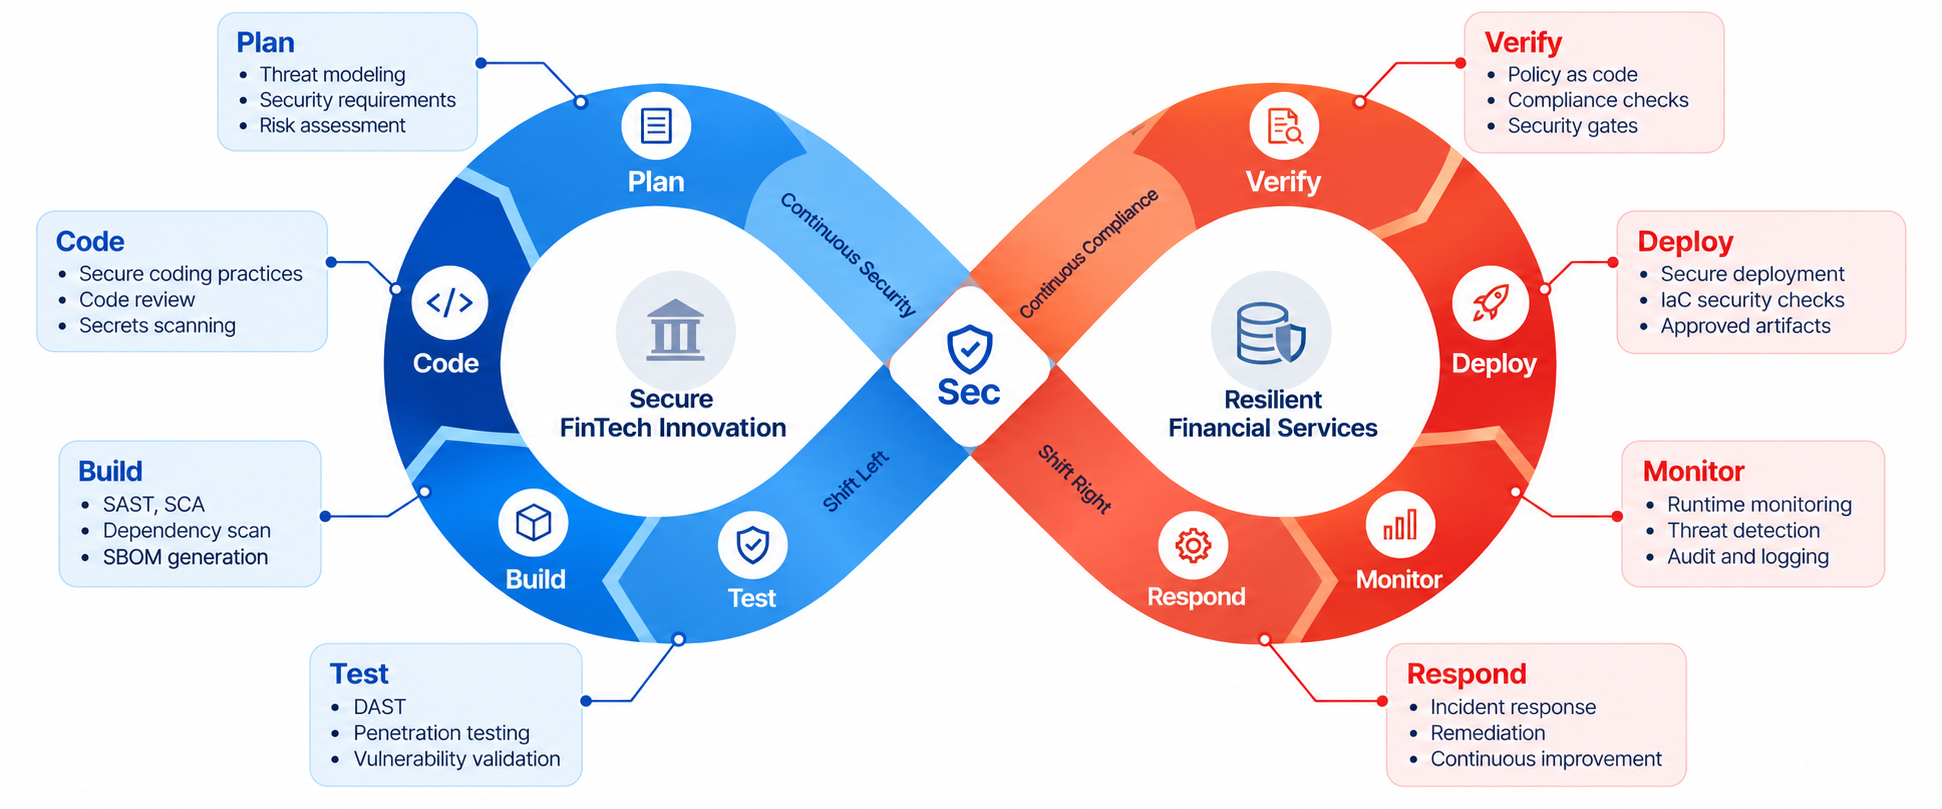
The pipeline should apply controls according to risk rather than adding every available security scanner to every stage.
AWS’s Financial Services Industry Lens recommends security testing throughout the software development lifecycle and highlights automated remediation and vulnerability management as part of a DevSecOps approach for financial institutions.
Drawing on Azilen’s FinTech engineering expertise, these 10 practices show how development and security teams can apply DevSecOps in FinTech to strengthen security, support compliance, and secure software delivery.
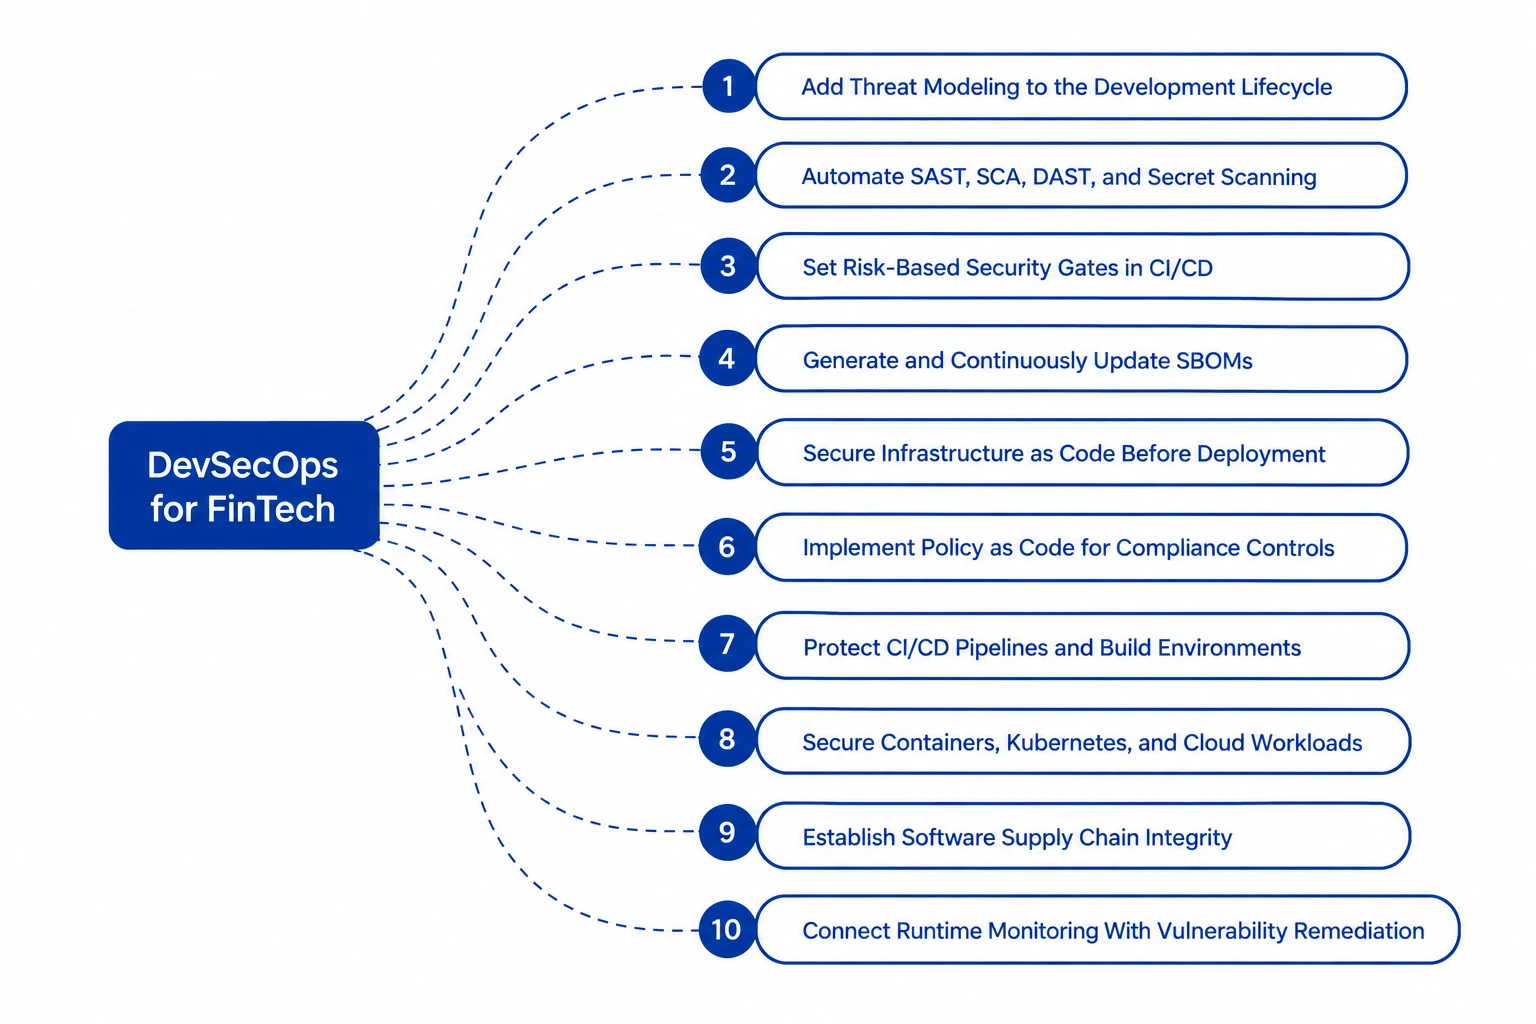
Threat modeling helps FinTech teams identify security risks before implementation.
Teams can map sensitive data, trust boundaries, authentication flows, APIs, and critical transactions, then define security requirements before code reaches the pipeline.
For payment, banking, and financial applications, this can help prioritize controls around high-impact workflows rather than applying identical security checks everywhere.
NIST recommends integrating secure development practices into the SDLC to reduce vulnerabilities and address their underlying causes.
SAST can identify weaknesses in source code, SCA can detect vulnerable dependencies, DAST can test running applications, and secret scanning can identify exposed credentials.
Running these checks through CI/CD gives developers faster feedback and creates repeatable security controls across releases.
A security gate should prevent high-risk issues from progressing toward production while allowing teams to manage lower-risk findings through defined remediation workflows.
FinTech teams can establish thresholds based on severity, exploitability, application criticality, and regulatory requirements.
This creates a controlled release process without making every security finding an automatic deployment blocker.
A Software Bill of Materials provides a machine-readable inventory of the components within an application.
FinTech teams can generate SBOMs during builds and connect them with vulnerability monitoring to quickly identify affected applications when a dependency vulnerability emerges.
GitLab supports automated SBOM generation and dependency analysis within CI/CD workflows.
Infrastructure configuration can introduce security issues just like application code.
Scan Terraform, Kubernetes manifests, cloud templates, and other IaC files before deployment to identify exposed resources, excessive permissions, insecure network configurations, and other policy violations.
Catching these issues in the pipeline gives teams an opportunity to correct infrastructure before it reaches production.
Policy as Code converts selected security and compliance requirements into machine-enforced rules.
For example, a pipeline can require approved artifacts, prohibit certain configurations, or enforce security checks before production deployment.
This approach makes controls more consistent and creates repeatable evidence across releases.
The CI/CD pipeline itself is part of the software supply chain.
FinTech teams should protect source repositories, build runners, credentials, deployment permissions, and artifact repositories through controls such as least-privilege access, protected branches, isolated build environments, and strong authentication.
GitLab’s supply-chain guidance also highlights approval rules, secret detection, signed commits, isolated builds, and artifact controls.
For containerized FinTech applications, security needs to cover both the image and the environment running it.
Scan container images for known vulnerabilities, use trusted base images, control Kubernetes permissions, secure secrets, and continuously assess workload configurations.
Red Hat recommends maintaining current container images and addressing known vulnerabilities before production use.
Knowing what is inside an application is only one part of supply-chain security. Teams also need confidence in where an artifact came from and how it was built.
Artifact signing, provenance, protected build environments, and verification controls can help detect unauthorized or tampered software.
GitLab’s SLSA implementation, for example, supports provenance generation and signing to strengthen artifact integrity.
Security controls should continue after deployment.
Connect application, infrastructure, and security monitoring with vulnerability management so teams can identify issues in production, prioritize them based on business impact, and route remediation back into development workflows.
This creates a feedback loop between production → security → development → deployment, which keeps the FinTech DevSecOps lifecycle continuous.
Adoption of DevSecOps for FinTech works better when organizations start with their existing architecture, development process, and risk profile.
A useful maturity model can help organizations determine where to begin.
Level 1 — Reactive: Security reviews happen primarily after development.
Level 2 — Integrated: Security scanners become part of CI/CD.
Level 3 — Automated: Security policies, vulnerability management, and compliance checks become automated.
Level 4 — Continuous: Security extends from development through production with continuous monitoring and remediation.
Level 5 — Risk-Based: Security controls dynamically reflect application criticality, business risk, regulatory requirements, and the organization’s threat environment.
The goal is to create a delivery environment where security controls become standardized and repeatable while teams retain appropriate risk-based decision making.
Before scaling DevSecOps for FinTech product environment, assess whether your engineering organization has the following capabilities:
DevSecOps for FinTech becomes particularly relevant when engineering teams encounter recurring security and delivery challenges such as:
→ Security testing happens late in the release cycle
→ Vulnerability remediation creates release delays
→ Compliance evidence requires substantial manual effort
→ Development teams use inconsistent security controls
→ Cloud and Kubernetes environments are expanding
→ Third-party dependencies are difficult to track
→ Multiple CI/CD pipelines follow different security standards
→ Security teams lack visibility into software delivery
→ New regulatory requirements require changes to engineering controls
→ Engineering leadership wants stronger security controls without creating a separate manual review process for every release
At this stage, an external DevSecOps partner like Azilen can help assess the existing environment, define the target architecture, select appropriate controls, integrate security into CI/CD, and establish repeatable compliance workflows.
FinTech engineering requires a balance between product delivery, security, scalability, and regulatory expectations.
Azilen helps FinTech product companies design and implement software delivery environments with security integrated across application development, cloud infrastructure, CI/CD, and operational workflows.
Our approach can cover:
Evaluate the existing SDLC, CI/CD pipelines, infrastructure, security controls, and compliance requirements.
Integrate automated security testing and policy checks into development and deployment pipelines.
Build security controls across cloud infrastructure, containers, Kubernetes, and Infrastructure as Code.
Improve visibility across dependencies, artifacts, SBOMs, and software delivery workflows.
Map applicable security requirements to repeatable engineering controls and automate evidence collection where appropriate.
Extend security practices into production through monitoring, vulnerability management, and remediation workflows.
With experience across FinTech software development, Azilen can work with existing engineering environments and technology stacks to introduce DevSecOps practices around the systems teams already operate.


 10 mins
 16 mins

"*" indicates required fields

5432 Geary Blvd, Unit #527 San Francisco, CA 94121 United States
320 Decker Drive Irving, TX 75062 United States

6d-7398 Yonge St,1318 Thornhill, Ontario, Canada, L4J8J2
71-75 Shelton Street, Covent Garden, London, United Kingdom, WC2H 9JQ

Hohrainstrasse 16, 79787 Lauchringen, Germany

12, Zugerstrasse 32, 6341 Baar, Switzerland

5th floor, Bloukrans Building, Lynnwood Road, Pretoria, Gauteng, 0081, South Africa

12th & 13th Floor, B Square-1, Bopal – Ambli Road, Ahmedabad – 380054
B/305A, 3rd Floor, Kanakia Wallstreet, Andheri (East), Mumbai, India



 Talk to Our
Consultants
 Chat with
Our Experts
 Write us
an Email
